
A technology failure at a small law firm is never just a technology problem. Picture a Monday morning. The case files will not open. Email is down. A filing deadline is hours away. And a client is waiting on a wire that no one can confirm. A law firm also holds money, secrets, and deadlines at once. So one bad morning can become a malpractice exposure, an ethics complaint, and a lost client. Managed IT services for law firms exist to make sure that morning never arrives. They keep your practice secure, available, and confidential, without any partner needing to understand the technology underneath.
This guide is for the people who carry that risk: the managing partner, the office administrator, and the attorney who signs the checks. In plain terms, it answers the questions partners ask us first. For example, what does one breach or one lost filing day really cost? Why do attackers prefer small firms? And should you hire someone in-house, or hand the job to a team that runs law office IT every day?
⚖️ Want your firm secure, available, and confidential without hiring a tech team?
Wintive runs Microsoft 365 for small US law firms end to end. We protect client data, secure every device, automate backups, and we also document every safeguard your duty of confidentiality demands. It is also a flat monthly rate, with no long contract and no setup fee.
📅 Book a Free 30-Min Call | 💬 Chat on WhatsApp | See Our Plans →
🎯 The Three Risks Every Small Law Firm Faces in 2026
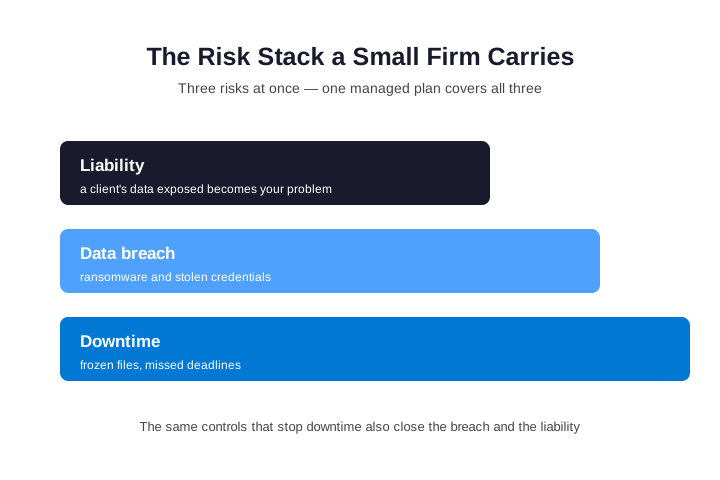
In short, a small law firm carries three risks at the same time. First, downtime. A single ransomware hit can freeze your documents, email, and billing for days. Every frozen hour is a missed deadline and lost billable work. Second, a breach of confidential client data. Case files and trust-account details are high-value targets, so attackers go after small firms on purpose. Third, an ethics and liability exposure. Your duty of confidentiality expects reasonable safeguards, and being small is not a defense. Managed IT services for law firms cover all three at once.
Where the real exposure actually sits
Look at the exposure the way a managing partner would. First, downtime hurts at once. For example, a frozen document system means missed filings, idle paralegals, and a judge who will not wait. Moreover, clients start to doubt that you can protect their matter. Second, a breach follows you for years. Once a privileged file leaks, state notification rules apply, and a bar inquiry may come next. Furthermore, you must explain the leak to every client affected.
Third, liability sits under both. Under Comment 8 to ABA Model Rule 1.1, competence includes the benefits and risks of the technology you use. Therefore, the table below pairs each risk with the work that removes it, and with the part Microsoft 365 already covers. Notably, it reads as a list of outcomes for a firm owner, not as a technical spec.
What managed IT services for law firms remove first
| The business risk (plain English) | What a managed plan handles for you | Where Microsoft 365 helps |
|---|---|---|
| A frozen morning that stops billable work | 24/7 monitoring and a recovery plan built around court deadlines | Cloud documents and email stay reachable from anywhere |
| A privileged file opened by the wrong person | Matter-level access, reviewed whenever staff join or leave | SharePoint and Teams permissions scoped per matter |
| A stolen password used to read client data | A second login step for every attorney and assistant | Multi-factor sign-in included in every license |
| Ransomware locking your case files | Encrypted laptops plus off-site backups of every matter | Version history that rolls back locked files |
| A wire instruction quietly altered by an attacker | Impersonation filters plus a call-back rule for wire changes | Anti-phishing rules that flag lookalike senders |
| An auditor or client asking what you protect | Activity logs kept for a bar or insurer inquiry | Audit search in Microsoft Purview |
Read that table through your ethics rules. For example, the stolen-password row is a Rule 1.6(c) problem, because it exposes client information. Similarly, the altered wire touches your duty to safeguard client funds in trust. In contrast, the frozen morning is a competence problem, since a court rarely moves a deadline for an office outage. You keep those duties. However, the daily work behind them moves to a dedicated team.
🛡️ Why Small Law Firms Are a Top Target
To begin with, many partners assume attackers chase only the giant firms. But in reality, the opposite is true. Specifically, a small firm holds exactly what criminals want. That means valuable data such as settlements, escrow funds, and client records. However, it rarely has a security team watching over it. Furthermore, a two-partner office faces the same threats as a national firm, and the same pattern hits regulated fields like healthcare. Consequently, the small firm is far easier to break into. That mix of high value and low defense is exactly why small firms are so often targeted.
How managed IT services for law firms close the gap
Consider how most breaches at law firms begin. Notably, the attacker is rarely a genius. Instead, it is usually one convincing email timed to a closing or a settlement. As a result, the attacker either redirects the funds or quietly reads privileged files. Moreover, no one reviews the mailbox rules or sign-in alerts day to day. So the intruder can stay inside for weeks. Legal IT support exists to close that gap before anyone exploits it.
In other words, the weak point is rarely the software. Instead, it is the lack of an owner. Therefore, the firms that sleep well share one trait: someone outside the firm watches their accounts every day, and that is the only job that team does.
💸 Wire Fraud Is the Threat Aimed at Your Trust Account
Wire fraud is the attack built specifically for law firms, so it deserves its own plan. The pattern is simple, and it is brutally effective. An attacker quietly watches a real-estate closing or a settlement. Then, at the last minute, they send an email that changes the payment details. Because the request looks routine, the money often leaves before anyone checks. And once a wire is gone, it is almost never recovered. So this single risk can drain a client’s funds and your reputation in one afternoon.
The danger is worse for a small firm, because the same person often handles the email, the trust account, and the deadline. As a result, there is no second pair of eyes when a fake request lands. Notably, attackers know this, so they aim at small practices on purpose.
How managed IT services for law firms stop the fraud
Good legal IT support closes this gap on several fronts at once. First, it locks every inbox behind a second login step, so an attacker cannot take one over. It also adds impersonation filters that flag a lookalike sender before anyone replies. Then it builds a simple habit into the firm: any change to payment details is confirmed by phone, on a known number. Because the controls and the habit work together, the fake request fails even when it looks convincing. Layered managed security services also catch most of these attempts early.
Above all, this is a problem you solve once and then monitor forever. So the firms that never lose a wire are simply the ones that put these controls in place early. And because every safeguard is documented, a clean answer is ready the moment a client or an insurer asks about it.
⚖️ Client Confidentiality Is a Business Risk, Not an IT Checkbox
To begin with, most partners treat confidentiality as an ethics-manual line. In truth, it is a financial and reputational risk with teeth. The ABA Model Rules expect every lawyer to make reasonable efforts to prevent disclosure of client information. Many states now read that too as a duty to use real safeguards. When something goes wrong, a bar inquiry does not ask whether you meant well. So it asks what protections you had in place. And then it asks you to show them. If you cannot, the exposure climbs fast.

How managed IT services for law firms meet the duty
Crucially, this duty does not scale down because you are small. In fact, the same core expectations apply to a solo and to a hundred-attorney firm. You must first limit who can open a matter. Second, you must add a second lock to logins, so a stolen password is not enough. You must also keep records safe and recoverable. Finally, you must notice and report when something goes wrong, and keep an audit-ready compliance checklist to prove it. None of that is optional.
💡 What we see across the firms we manage: The breach almost never starts with a brilliant attack. Instead, it starts with one busy associate clicking one convincing email near a deadline. From there, the attacker then moves through matters that were never locked down. Nobody was watching, so it spread quietly. Specifically, the firms that stay safe are not the ones with the most software. They are the ones where someone owns the email, the devices, and the backups every day. That responsibility is what Wintive provides, and it is the part most legal IT solutions quietly leave to you.
So this is the part that matters for a decision-maker. Importantly, you do not need to become a security expert. However, you do need someone to close that open door first. That is the entire purpose of a managed plan for a firm. It puts a responsible team between your privileged data and the people trying to steal it.
🧩 What Managed IT Services for Law Firms Actually Cover
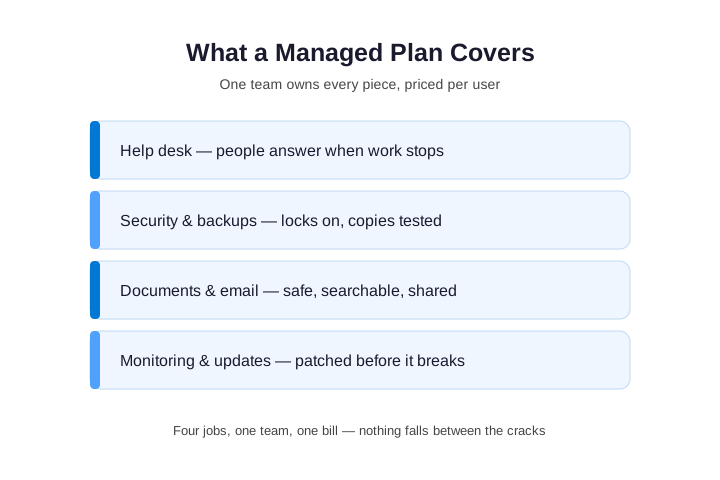
In practice, managed IT services for law firms turn routine technology work into one service, priced per user. For example, the help desk answers when a paralegal cannot open a matter before a filing. Meanwhile, security runs in the background on every laptop and phone that touches client files. In addition, backups cover the document store, email, and billing data. Instead of juggling vendors, you get one team, the way managed IT support services work for any small business. As a result, less billable time leaks into IT problems.
Where legal IT support goes beyond fixing laptops
Furthermore, good law firm IT support does more than fix laptops. Notably, it secures the document system where your matters live. In addition, it protects the email that handles wire instructions. And it keeps your practice tools, such as Clio or NetDocuments, connected to Microsoft 365. Moreover, it handles the unglamorous work that prevents disasters. That means patching software the day a fix ships. It means watching for warning signs around the clock. And it means testing the backups, so a restore actually works.
Critically, the security layer is now part of the core service. So it is not an add-on. As a result, multi-factor login, encrypted devices, controlled sharing, and monitoring all ship together. That bundle turns a pile of licenses into a firm that can answer a client security questionnaire with confidence.
🔐 Which Plan Your Firm Actually Needs
To begin with, protection should follow your practice, not a price list. For example, an estate-planning boutique and a firm that closes commercial deals face very different threats. Therefore, a good provider sizes the plan to two things: how sensitive your matters are and how much money moves through your trust account. Consequently, nobody pays for the heaviest package by default.
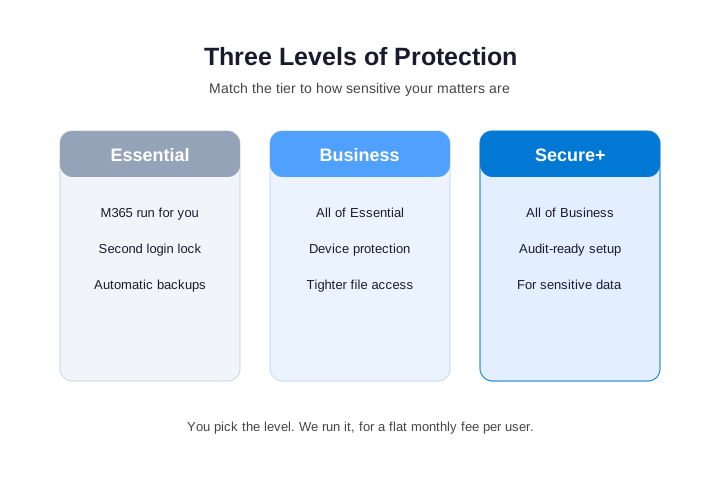
Importantly, the gap between tiers is rarely the software. For example, a solo family-law practice and a real-estate firm can hold the same licenses. However, the real-estate firm moves escrow money every week, so it needs stricter email rules and closer monitoring. Therefore, choose the tier by the money and the matters you handle, not by the logo on the invoice.
💼 Hire In-House or Outsource? The Real Math
To begin with, few small firms can justify a full-time IT hire. First, one salary plus benefits costs more than most partners expect. Moreover, one person cannot master networking, security, and your document system at once. Worse, that person becomes a single point of failure during a trial or a holiday. In contrast, a managed plan gives you a whole team for less than one salary.
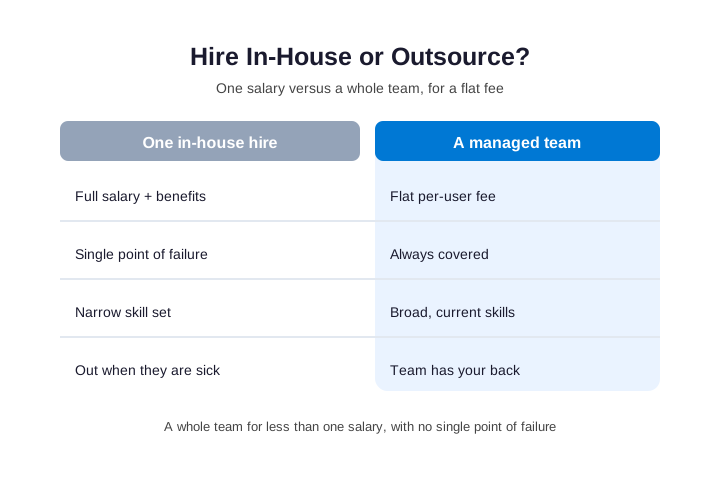
Additionally, a provider that serves several firms has already met your future problems, from a broken document profile to a failed e-filing upload. For example, it knows how Clio, NetDocuments, and Outlook work together. Furthermore, the model can support an existing office manager. In that case, co-managed IT support adds monitoring, security, and after-hours cover. Consequently, a trial week or a vacation never leaves the firm without help.
💰 What It Costs: Predictable, Per-User Pricing
In practice, most providers price legal IT services per user, per month. For example, four attorneys and three staff means seven users. That rate covers the help desk, security, backups, and monitoring. As a result, IT becomes a fixed budget line, like rent or your malpractice premium. For a small firm, it usually costs a fraction of one IT salary, with no surprise project bill.
| What you are buying | The break-fix way | The managed way |
|---|---|---|
| How you pay | Hourly, after something has already failed | One flat fee per user, each month |
| When help arrives | After the deadline is already at risk | Before most problems reach you |
| Security and backups | Often skipped to save money | Included and tested as standard |
| Your exposure | One bad day can rival a year of fees | Predictable cost, contained risk |
What flat-rate legal IT services really buy you
Crucially, flat-rate pricing changes behavior, not just the budget. Notably, the fee stays the same when an associate calls three times in a week. So people report problems early, before they reach a client. Therefore, the provider earns its fee by preventing incidents rather than billing for them. That is the incentive a busy firm wants.
It also helps to compare the fee to the real alternative, not to zero. For example, one lost day for five timekeepers billing six hours each at $300 erases $9,000 of billable time. Similarly, one diverted settlement wire can cost more than a decade of fees, and a claim may follow. Therefore, the real question is whether your firm can absorb the loss the fee prevents.
⚠️ The Mistakes That Quietly Sink Small Firms
In practice, most IT failures at small firms come from a few habits. First, the firm assumes Microsoft 365 is secure out of the box, while most protections ship switched off. Second, a departing associate keeps access to email and matters for weeks. Third, one office manager holds every password, so a single resignation can lock the firm out. Finally, nobody has ever restored a matter from backup, so the first real test happens during a crisis.
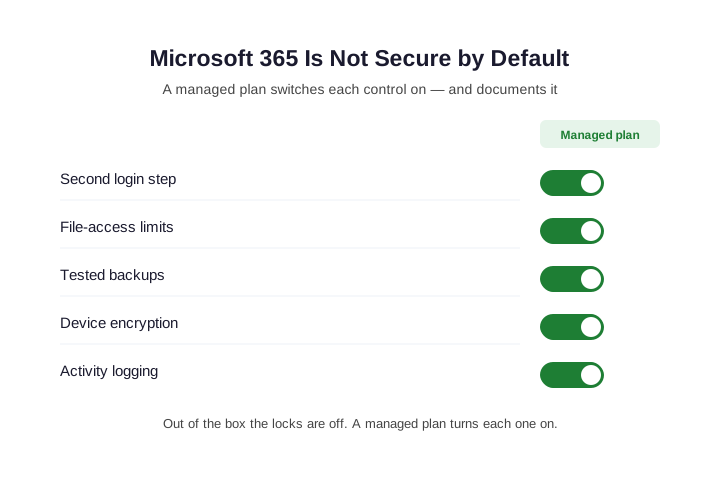
Furthermore, each gap takes hours to close, not weeks, once someone owns it. For example, an offboarding checklist ends the departed-associate problem for good. As a result, a good provider closes and documents every gap, so you can answer a client questionnaire at once.
🔍 The single most common gap we find: A firm proudly shows us its Microsoft 365 subscription, believing the job is done. Then we look inside the account. We find no second login step. We find matters shared far too widely. And we find a backup no one has ever tested. The licenses were real, but they protected nothing on their own. These gaps fail silently for months, until an attacker or a client audit finds them. Closing that exact gap is the core of good law firm IT security.
✅ The Managing-Partner Checklist Before Choosing a Provider
Before you sign with any provider, run a short test. It shows quickly whether they understand a law office. First, ask whether they document each safeguard, since a client or an insurer may ask for proof. Second, ask how they remove access when an associate leaves, because stale accounts cause many leaks. Third, ask how often they test a restore of your matter files. Finally, ask which practice tools they support. A provider who has never touched Clio or NetDocuments will slow every matter down.
Above all, these questions reveal experience quickly. Specifically, a provider who has supported firms answers with real tools and real examples. In contrast, vague talk about best practices usually means you would train them on your own billable time.
🧮 Switching Providers: What the First Quarter Looks Like
How managed IT services for law firms handle the first 90 days
Switching providers feels risky, so many firms delay it for years. In practice, a careful onboarding starts with an inventory, not with changes. First, the new team reviews every user account, including former associates who still have access. Next, it maps who can open which matters and checks the rules on the inbox that handles trust-account wires. Within two weeks, it closes urgent holes, such as a missing second login step. As a result, managed IT services for law firms prove their value before the first invoice arrives.
Good managed IT services for law firms never change everything on day one. Instead, they plan around your court calendar, so no change lands during a trial week or a filing deadline. For example, a new login step goes to one practice group first, then to the whole firm. Meanwhile, attorneys keep billing as usual. Therefore, most staff notice only that logins and file searches feel faster.
What you should measure after the move
Track a few numbers from week one, so you judge the switch on facts. For example, measure how long it takes to recover a deleted matter folder, and how many tickets arrive before a filing. In addition, note how fast the firm answers a client security questionnaire. Managed IT services for law firms should cut that from days to hours, since the evidence already sits on file. Similarly, the cyber insurance renewal should stop feeling like an exam.
Finally, review the relationship every quarter, not once a year. For example, a review can cover a new associate, a second office, or a client that now demands encrypted email. It is also the moment to set rules for AI tools, which ABA Formal Opinion 512 addresses. That way, managed IT services for law firms follow the growth of the practice. Overall, the technology fades, and the legal work takes over again.
None of this needs a large budget. Instead, it needs a partner who understands how a law office runs, from client intake to the final invoice. After the first quarter, each review gets shorter. Consequently, managed IT services for law firms turn that stability into more billable hours.
📚 More for US Law Firms
⚖️ Ready to protect your firm and stop worrying about IT?
Wintive runs your Microsoft 365 the way a law firm needs it. Client data is locked down. Every device is protected. Backups are automatic. And every safeguard is switched on and documented. It is one flat monthly fee per user. No long contract. No surprise bills.
❓ Managed IT Services for Law Firms: Frequently Asked Questions
They are an ongoing service where one provider runs the technology of your firm for a flat monthly fee. That covers the help desk, security, backups, and updates for email, documents, and practice software. The goal is to keep matters available and client information confidential, as ABA Model Rule 1.6(c) expects.
A typical plan includes a help desk, device monitoring, patching, and tested backups. It adds multi-factor login and email filters that catch fake wire requests. It also covers onboarding and offboarding, so a departing associate loses access the same day. Most providers bill per user per month.
Most providers charge a flat fee per user, per month, so the cost follows your headcount. For example, a firm of six people pays for six users. No project bill arrives after an outage. Over a year, the fee usually costs less than a single breach or one diverted wire.
They limit who can open each matter and add a second login step. Devices are encrypted and backups are tested. They also document each safeguard, so you can show a client or an insurer. That is how a firm meets its duty of confidentiality in practice, not just on paper.
More questions about managed IT services for law firms
Yes. Co-managed support means a provider works alongside your own staff rather than replacing them. The provider adds monitoring, security, and after-hours cover. Your internal person keeps the day-to-day relationships. It suits growing firms that want backup without losing their contact.
A good provider keeps your practice software, such as Clio or NetDocuments, connected to Microsoft 365. As a result, matters, documents, and email work as one system. A single team owns the whole setup, instead of pointing fingers.
They close the gaps behind most incidents at small firms: weak logins, stale accounts, fake wire requests, and untested backups. They also keep evidence of each control ready for client security questionnaires and cyber insurance renewals. The result is fewer incidents and fewer lost billable hours.